Red Team Deep Dive: DistCC Remote Code Execution
2026-09-10 · 2 min read
Assignment Scope
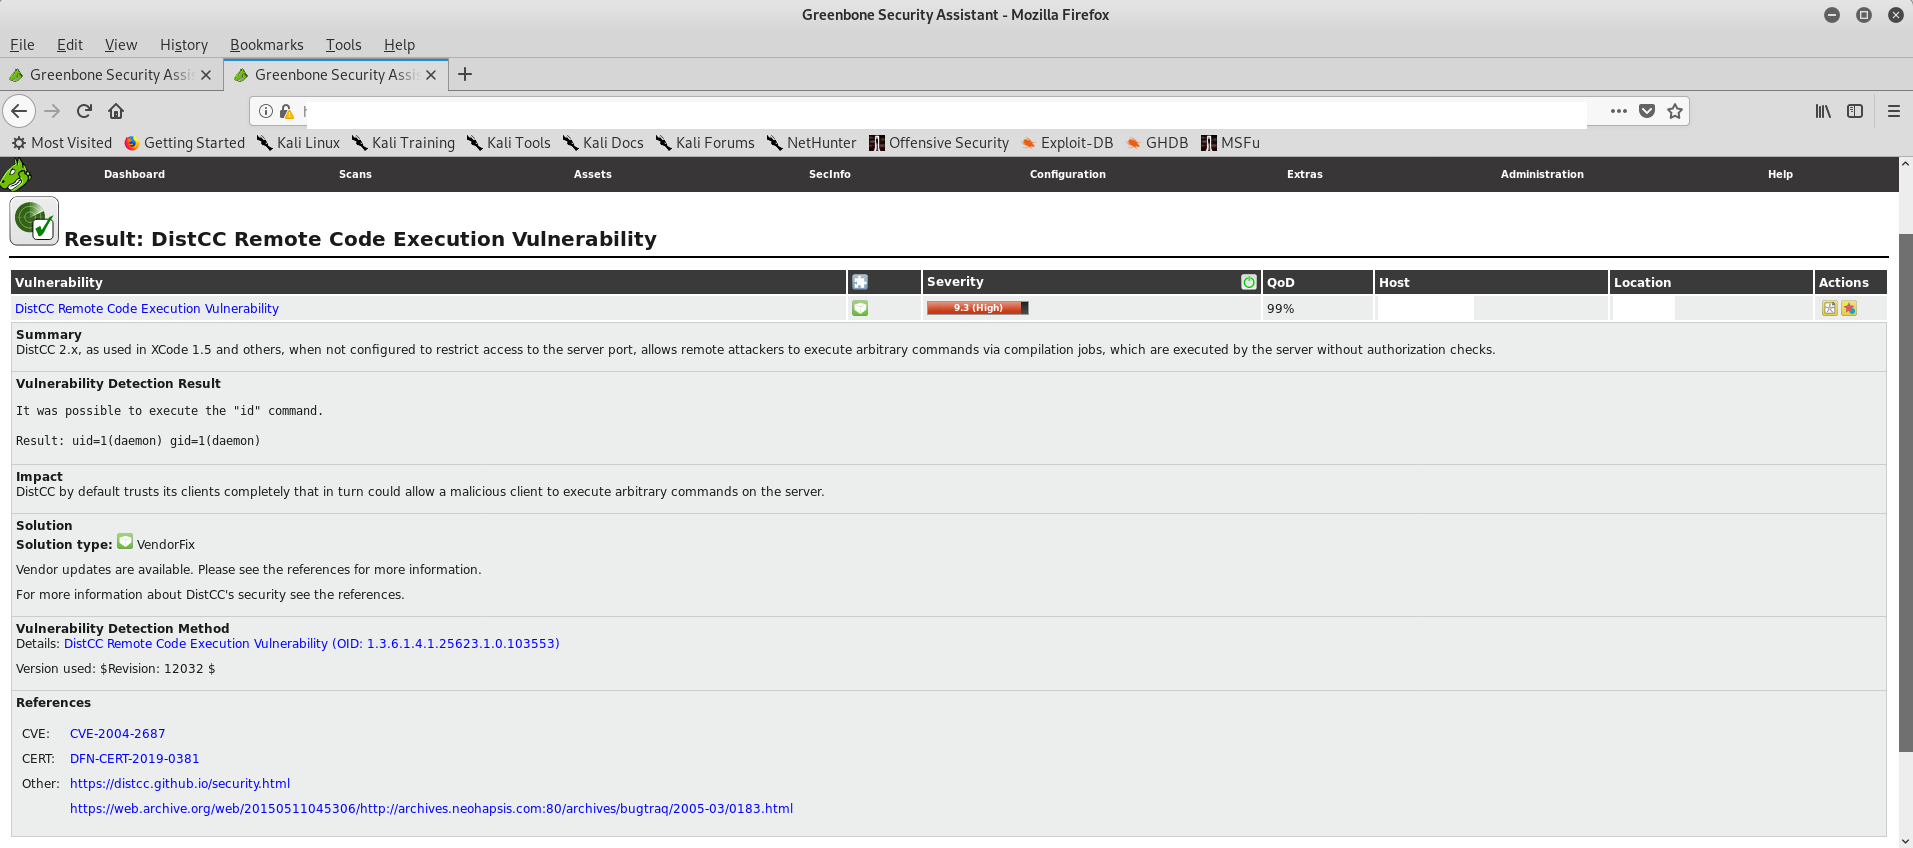
For this assignment, my red team is deep-diving into the vulnerabilities found in this scenario’s client machine. Each of us chose an individual vulnerability from our OpenVAS scan of the client’s machine — I picked the DistCC Remote Code Execution Vulnerability, CVE-2004-2687.
Vulnerability Overview
DistCC is a software development tool for speeding up compilation by distributing the computing workload across servers over the network. By default, DistCC 2.x does not restrict access to the server port. This allows attackers to execute arbitrary commands remotely, effectively acting as a developer using the tool.
CVE Details
| Field | Value |
|---|---|
| CVE | CVE-2004-2687 |
| CVSS | 9.3 |
| Severity | High |
DistCC 2.x, as used in Xcode 1.5 and others, when not configured to restrict access to the server port, allows remote attackers to execute arbitrary commands via compilation jobs, which are executed by the server without authorization checks [2].
Screenshot 4a — OpenVAS Findings
Why This Matters to the Customer
The DistCC vulnerability presents a serious threat to Hotel Dorsay’s business continuity and compliance. If exploited, a malicious actor could compromise:
- Confidentiality: of the hotel’s guests, employees, and possibly their financial information
- Integrity: of the hotel’s IT and communication systems by controlling and/or altering door lock passkeys, among other things
- Availability: by encrypting the system, essentially performing a denial-of-service (DoS) attack
Nmap Verification
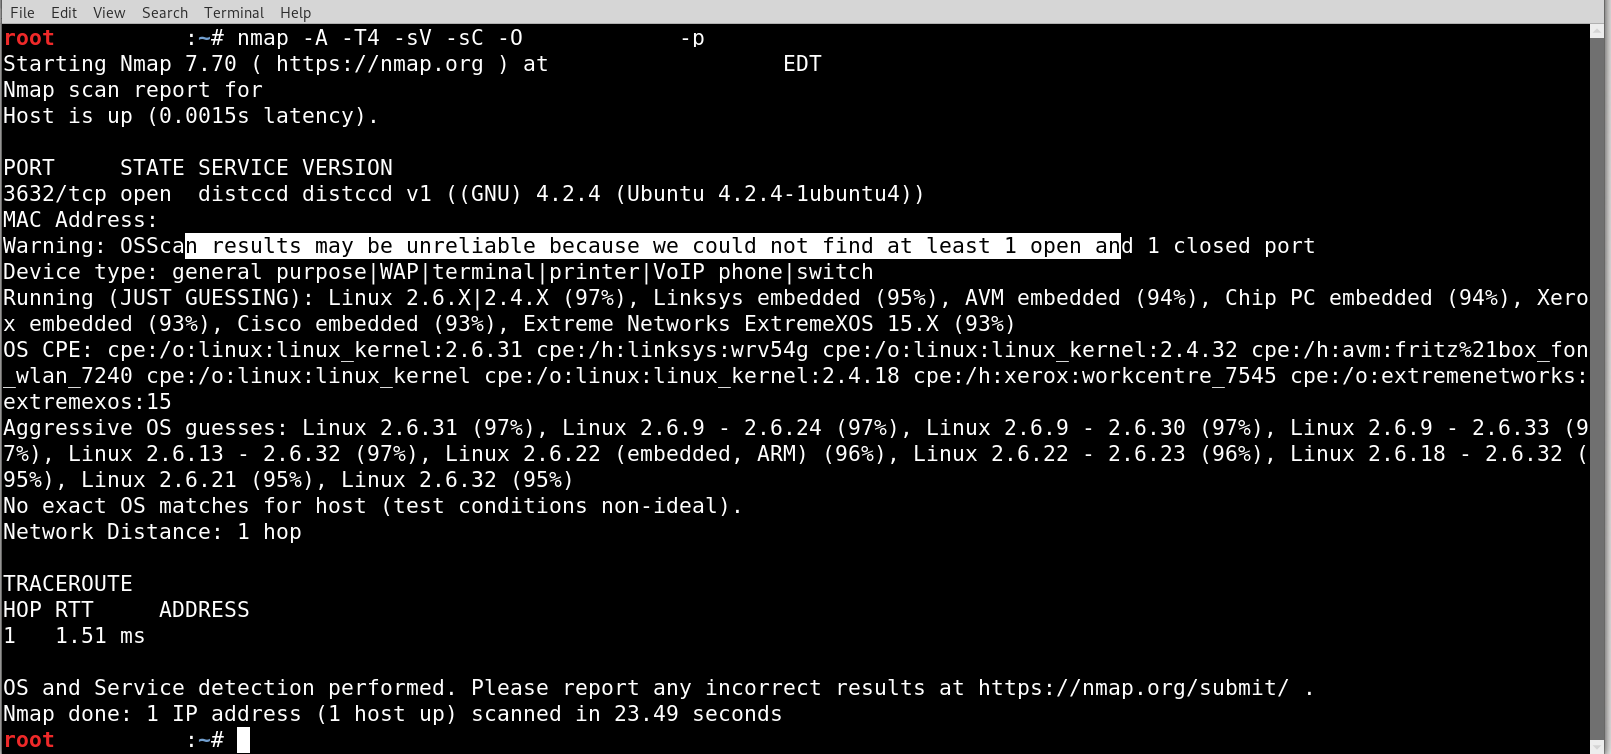
To verify the vulnerability, I performed a targeted Nmap scan. This command uses -A for an aggressive scan, -T4 for faster scanning speed, -sV for version detection, -sC to run Nmap’s default scripts, and -O for operating system detection.
nmap -A -T4 -sV -sC -O <target-ip> -p 3632
Screenshot 4b — Nmap Verbose Output
Analysis
The Nmap scan confirms the OpenVAS vulnerability finding. The scan shows that port 3632/tcp is open and running DistCC as a service. It also reveals additional information: the service protocol version, that the client machine is running Ubuntu, and the system’s MAC address.
Remediation
The quickest and easiest fix is updating to the current release of DistCC 3.3+ [1]. If the current version of the service is mission-critical, implementing an allowlist on the server, or using a VPN to reach the service, would mitigate the vulnerability.
References
[1] M. Pool, distcc: Distributed Builds for C, C++ and Objective C [Online]. Available: https://github.com/distcc/distcc [Accessed: Sep. 10, 2026].
[2] National Institute of Standards and Technology, “CVE-2004-2687 Detail,” National Vulnerability Database. [Online]. Available: https://nvd.nist.gov/vuln/detail/cve-2004-2687 [Accessed: Sep. 10, 2026].